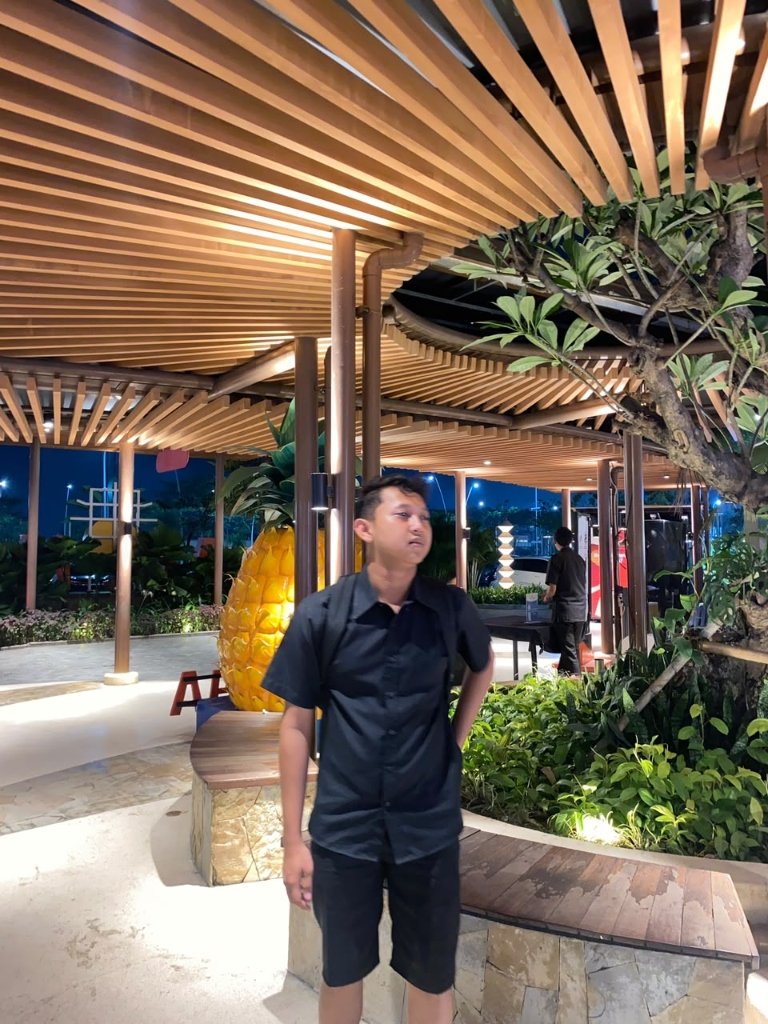
root@fahmi_haxor:~# whoami
root@fahmi_haxor:~# –
OFFENSIVE SECURITY ENGINEER

Zul Fahmi Rizki

< Penetration Tester Bug Hunter Developer />

Passionate offensive security engineer specializing in identifying and exploiting system vulnerabilities to strengthen organizational security posture.

0
Years Exp
0
Bugs Found
0
Gov Certs
0
CVEs Tracked
SCROLL DOWN

About Me

Zul Fahmi Rizki
ONLINE — READY TO HUNT
☡ ETHICAL HACKER ◆ BUG HUNTER
NAME Zul Fahmi Rizki
ALIAS FAHMI_X12
ORIGIN Banten
STATUS Active Bug Hunter
/* origin_story.exe — decrypting... */

Saya adalah Security Researcher & Bug Hunter asal Banten. Perjalanan saya di dunia siber dimulai bukan dari bangku akademik — melainkan dari rasa ingin tahu yang tak terbatas sejak bangku SMP.

Di usia 14 tahun, saya mulai mendalami dunia website defacement dan teknik-teknik penetrasi sistem. Aktivitas ini membawa saya ke pengalaman yang keras — ditangkap aparat pada tahun 2020 dan diliput berbagai media nasional sebagai "Hacker Pelajar SMP dari Anyer".

Salah satu insiden yang menjadi sorotan adalah keterlibatan dalam peretasan sistem KPU Jember — sebuah momen yang menjadi titik balik penting dalam perjalanan hidup saya.

Pengalaman itu bukan akhir — melainkan awal dari transformasi. Saya belajar bahwa kemampuan yang sama bisa digunakan untuk melindungi, bukan merusak. Sejak saat itu, saya berkomitmen penuh pada jalur ethical hacking dan responsible disclosure.

> Current Focus Areas:
◆ Bug Bounty Hunting — Government & Private Programs
◆ Web Application Penetration Testing & OSINT
◆ Responsible Disclosure & Vulnerability Research
◆ Web Development (Frontend & Backend Security)
$ cat /var/log/origin_story.log
2018
💻

Awal Mula — Self-Taught Hacker

Mulai belajar coding dan keamanan siber secara otodidak. Berawal dari rasa penasaran bagaimana website bisa diretas, tanpa ada yang mengajarkan secara formal.

2019
☢

Era Defacement — Gray Hat Period

GRAY HAT

Aktif melakukan website defacement sebagai bentuk "eksistensi" di komunitas hacker underground. Meretas puluhan sistem termasuk sistem KPU Jember yang menjadi sorotan nasional.

2020
🔒

Ditangkap — Titik Balik

CRITICAL EVENT

Pada usia 14 tahun, ditangkap dan menjadi berita nasional sebagai "Hacker Pelajar SMP dari Anyer, Banten". Diliput BantenNews, Kompas, dan berbagai media. Moment ini menjadi turning point terpenting dalam hidup.

🔗 Lihat berita: BantenNews.co.id
2021
◆

Transformasi — Ethical Hacker

REFORMED

Memutuskan untuk mengubah haluan sepenuhnya ke ethical hacking dan responsible disclosure. Mulai aktif di platform bug bounty legal dan belajar dari komunitas keamanan siber.

2025 — 2026
🏆

Recognition — Government Bug Hunter

CERTIFIED

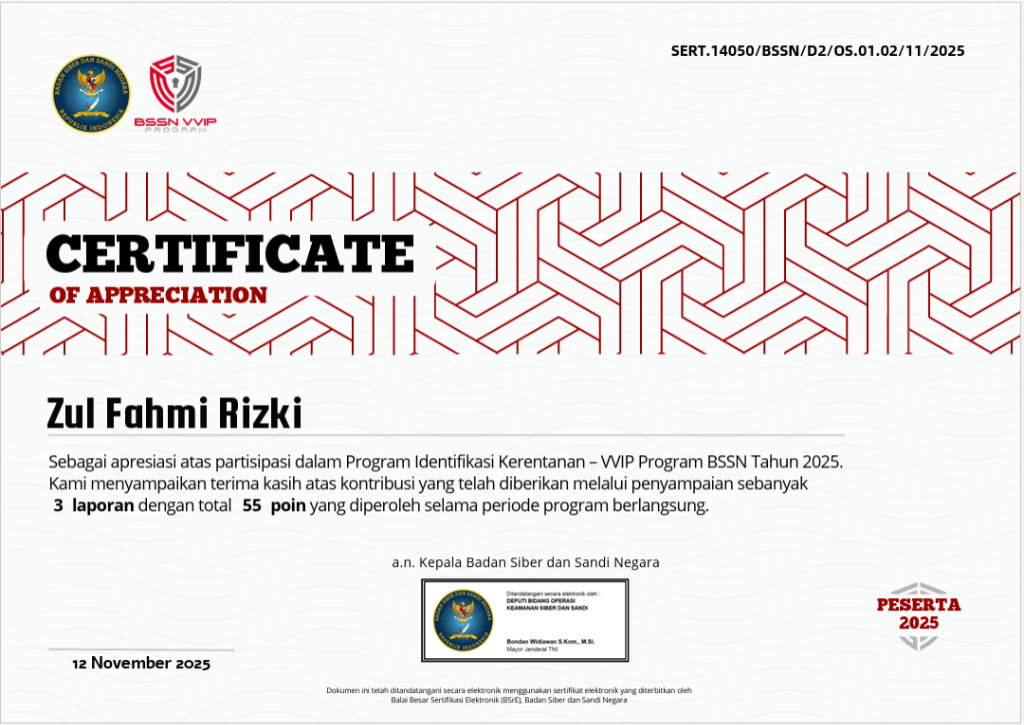
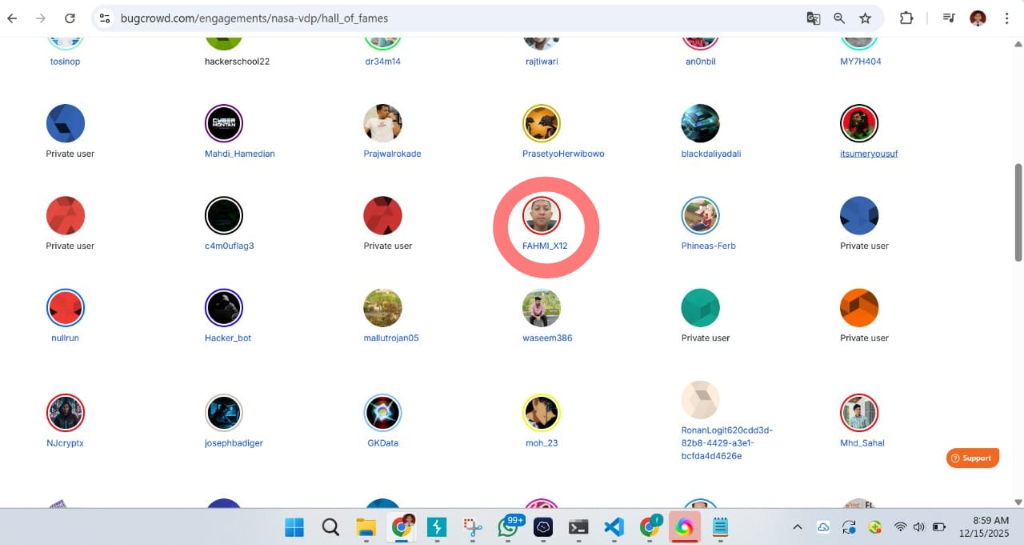
Diakui secara resmi oleh 10+ lembaga pemerintah Indonesia. Masuk NASA VDP Hall of Fame di Bugcrowd. Mendapat sertifikat apresiasi dari BSSN, Kominfo RI, ITB, UB, BMKG, KPI, dan lainnya.
Skills & Arsenal

⚙

Penetration Testing Tools

Burp Suite OWASP ZAP Nessus Metasploit Cobalt Strike Empire Nmap Masscan Zmap Wireshark tcpdump netcat sqlmap ffuf hashcat john
❮/❯

Programming & Scripting

Python95%
Bash / Shell Script92%
PHP88%
JavaScript / TypeScript87%
SQL / MySQL / PostgreSQL85%
Node.js / Express83%
Laravel / PHP Framework82%
jQuery / AJAX80%
HTML5 / CSS3 / Bootstrap90%
Ruby / Ruby on Rails72%
Go (Golang)68%
C / C++65%
FRAMEWORKS & LIBRARIES
Laravel Node.js Express.js jQuery React Vue.js Bootstrap Tailwind CSS Flask Django FastAPI REST API GraphQL WebSocket Redis MongoDB
△

Operating Systems & Platforms

⌫ Kali Linux
⌫ Parrot OS
⌫ Ubuntu / Debian
⌫ Windows Server
⌫ AWS / GCP
⌫ Docker / K8s
■

Security Domains

◇

Web Security

OWASP Top 10, XSS, SQLi, SSRF, XXE, IDOR, RCE, CSRF, Path Traversal, Business Logic

◇

Network Security

Network recon, MITM, lateral movement, pivoting, C2 frameworks, port scanning

◇

Mobile Security

Android/iOS pentesting, APK reversing, SSL pinning bypass, dynamic analysis

◇

Cloud Security

AWS IAM misconfig, S3 bucket abuse, metadata service exploitation, privilege escalation

Experience

2022 — Present

Offensive Security Engineer

Security Crash (Secrash)

Leading red team operations, conducting advanced penetration testing for enterprise clients across web, mobile, network, and ATM infrastructure. Founder and lead instructor of cybersecurity training programs.

Red Team Pentest Training
2020 — 2022

Senior Penetration Tester

Freelance / Bug Bounty

Active bug bounty hunter on HackerOne and Bugcrowd platforms. Discovered and responsibly disclosed critical vulnerabilities in major tech companies and government systems.

Bug Bounty HackerOne CVE
2018 — 2020

Security Researcher

Independent Research

Focused on vulnerability research, exploit development, and CTF competitions. Built custom tooling for automation of common pentest tasks using Python and Bash scripting.

Research CTF Exploit Dev

Bug Hunting Evidence

root@fahmi_haxor:~# ls -la ~/bug_hunting/certificates/
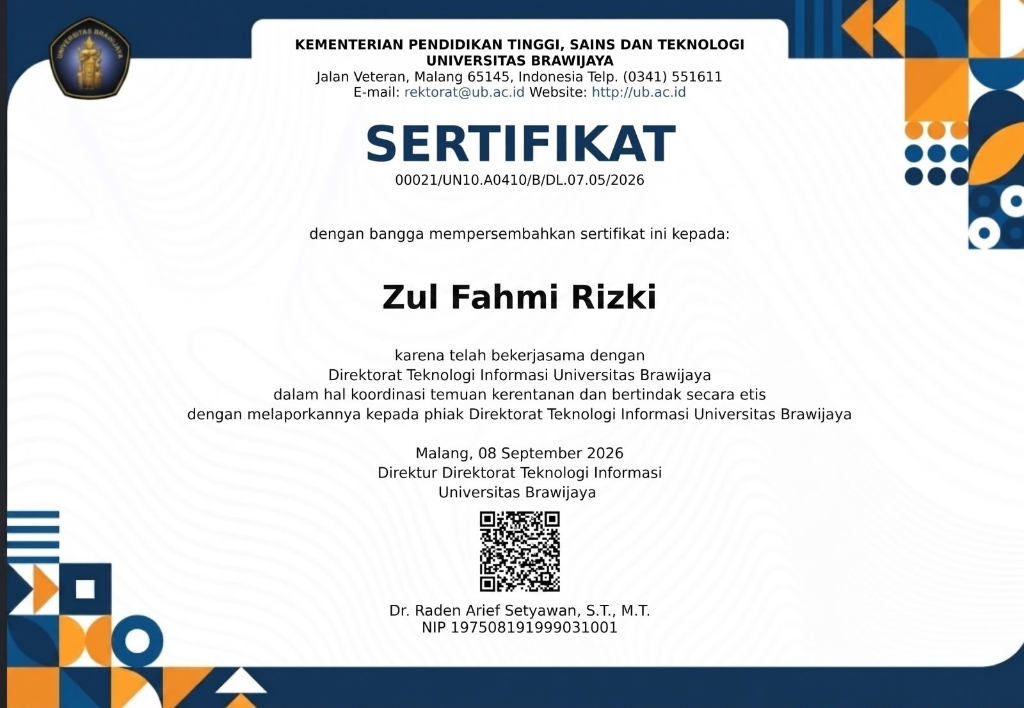
-rw-r--r-- cert_universitas_brawijaya.pdf Vulnerability Coordination — UB System
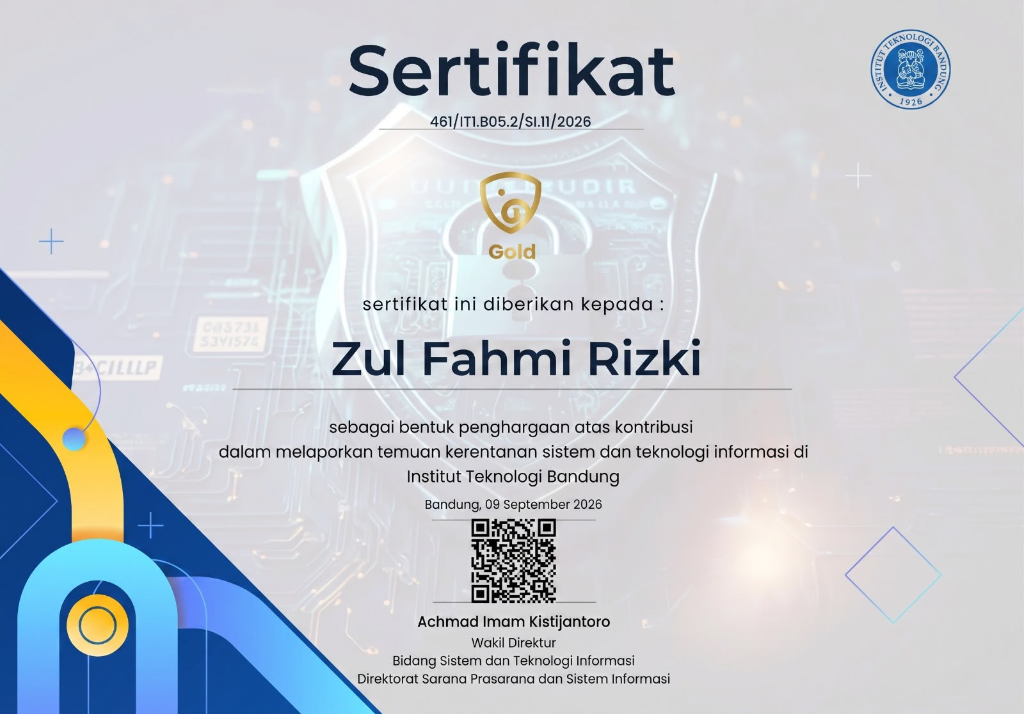
-rw-r--r-- cert_itb_gold.pdf Gold Award — ITB Security Reporting
-rw-r--r-- nasa_hall_of_fame.png NASA VDP Hall of Fame — Bugcrowd
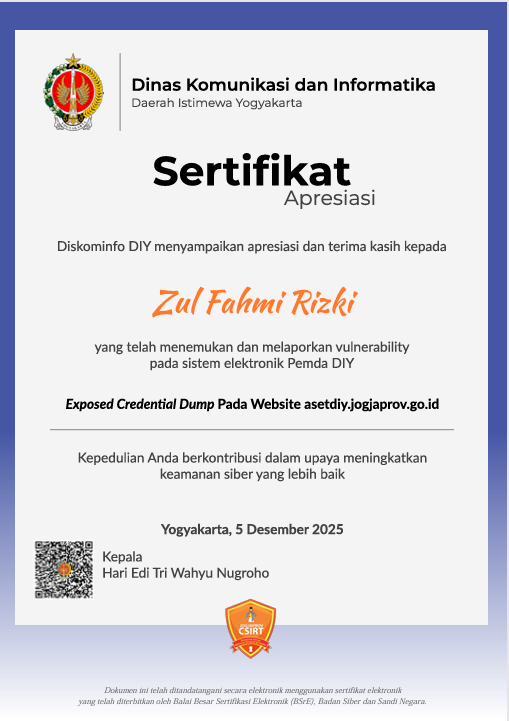
-rw-r--r-- cert_diskominfo_diy.pdf Exposed Credential Dump — Pemda DIY
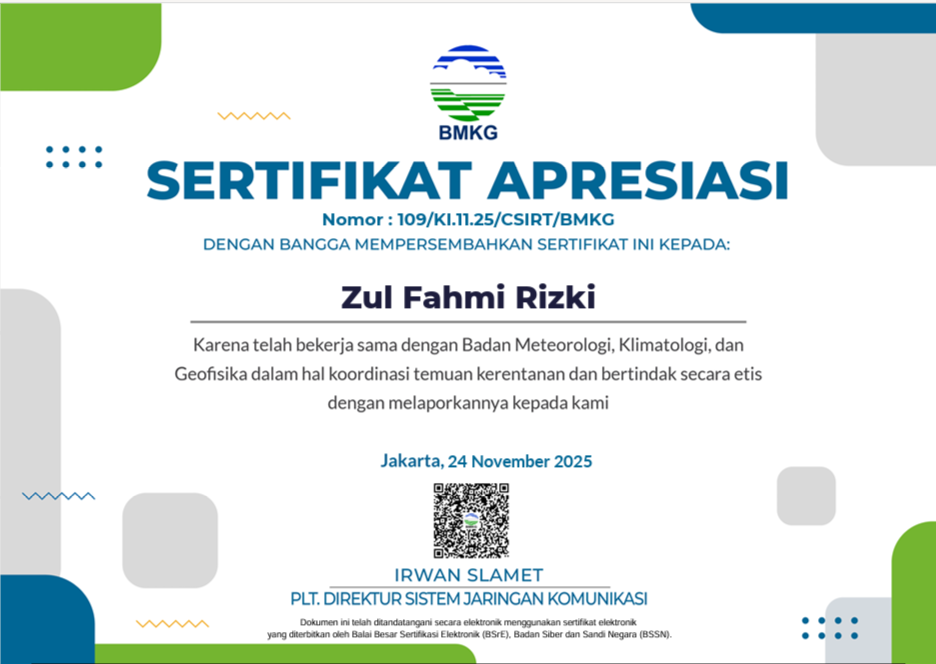
-rw-r--r-- cert_bmkg.pdf Vulnerability Coordination — BMKG
$ 5 files found –
⭐ GOLD AWARD
ITB Gold Certificate
🔍 CLICK TO VIEW
🏫 Institut Teknologi Bandung

Gold Security Certificate

Awarded Gold recognition for responsible disclosure of vulnerability findings in ITB's system and technology infrastructure.

ITB Gold Award Sep 2026
🏆 SERTIFIKAT
Universitas Brawijaya Certificate
🔍 CLICK TO VIEW
🏫 Universitas Brawijaya

Vulnerability Coordination

Recognized by Direktorat Teknologi Informasi UB for ethical coordination and responsible disclosure of security vulnerabilities.

Universitas Brawijaya VDP Sep 2026
☢ CRITICAL FIND
Diskominfo DIY Certificate
🔍 CLICK TO VIEW
🏠 Diskominfo DIY — Pemda DIY

Exposed Credential Dump

Found and reported critical Exposed Credential Dump on asetdiy.jogjaprov.go.id — Yogyakarta government asset system. BSSN-verified certificate.

Diskominfo DIY Gov Pentest Dec 2025
☀ APRESIASI
BMKG Certificate
🔍 CLICK TO VIEW
🌄 BMKG — Jakarta

Vulnerability Coordination

Recognized by BMKG for ethical vulnerability coordination and responsible disclosure to Indonesia's national meteorology agency.

BMKG Gov VDP Nov 2025
☢ SENSITIVE DATA
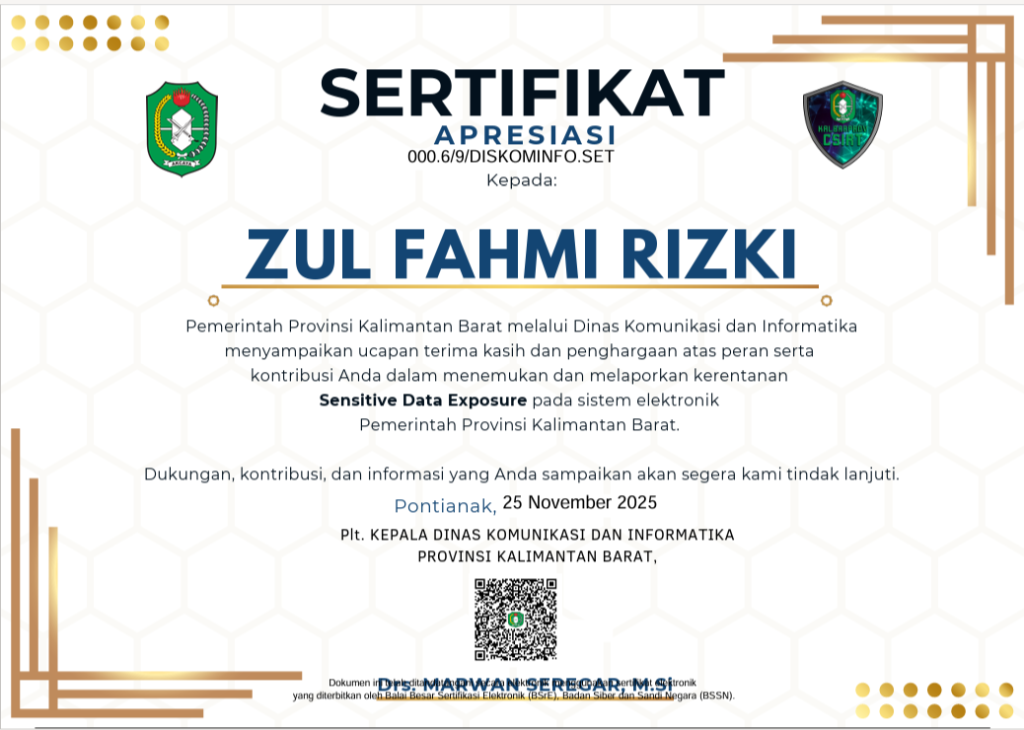
Diskominfo Kalbar Certificate
🔍 CLICK TO VIEW
🏝 Diskominfo — Kalimantan Barat

Sensitive Data Exposure

Menemukan dan melaporkan kerentanan Sensitive Data Exposure pada sistem elektronik Pemerintah Provinsi Kalimantan Barat. Sertifikat resmi berverifikasi BSSN.

Kalbar Gov Data Exposure Nov 2025
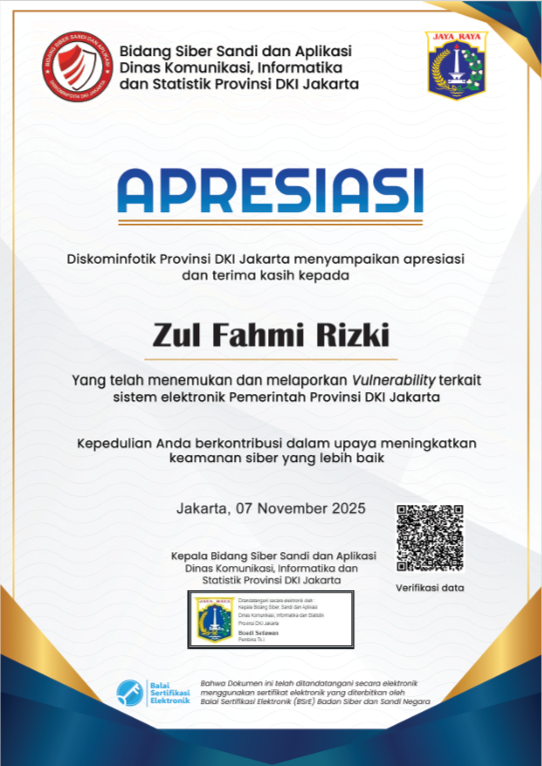
🏠 DKI JAKARTA
Diskominfotik DKI Certificate
🔍 CLICK TO VIEW
🏛 Diskominfotik — DKI Jakarta

Vulnerability Report — DKI Gov

Menemukan dan melaporkan kerentanan pada sistem elektronik Pemerintah Provinsi DKI Jakarta. Diverifikasi BSrE Badan Siber dan Sandi Negara.

DKI Jakarta Gov VDP Nov 2025
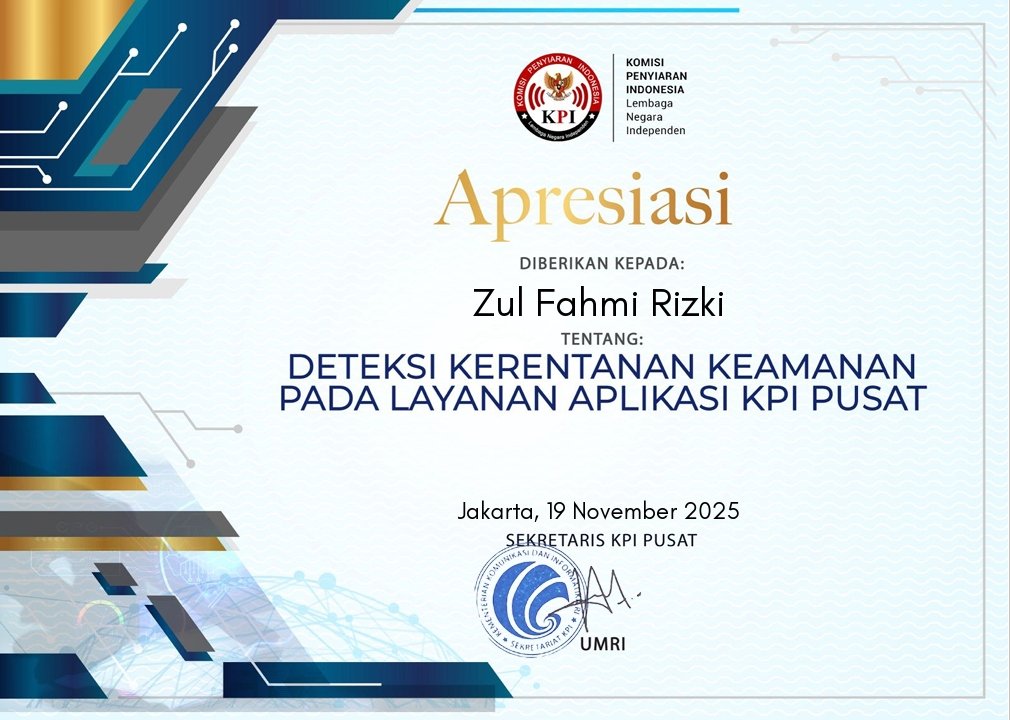
📿 KPI PUSAT
KPI Certificate
🔍 CLICK TO VIEW
📻 KPI — Komisi Penyiaran Indonesia

Deteksi Kerentanan Keamanan

Menemukan kerentanan keamanan pada layanan aplikasi KPI Pusat. Diakui secara resmi oleh lembaga negara independen Komisi Penyiaran Indonesia.

KPI Pusat App Security Nov 2025
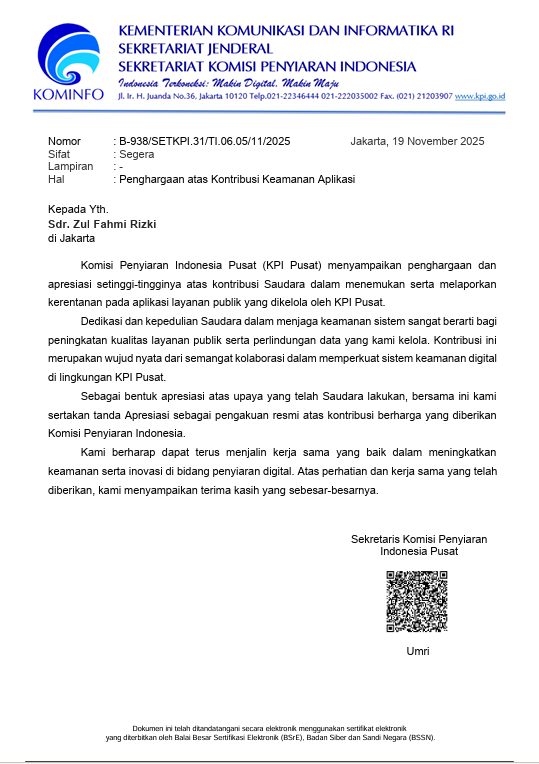
📄 KOMINFO RI
Kominfo Official Letter
🔍 CLICK TO VIEW
🏭 Kominfo RI — Surat Resmi

Penghargaan Kontribusi Keamanan

Surat resmi dari Kementerian Komunikasi dan Informatika RI sebagai pengakuan atas kontribusi berharga dalam peningkatan keamanan siber layanan publik.

Kominfo RI Surat Resmi Nov 2025

CVE Research 2026

root@fahmi_haxor:~# cat /var/log/cve-research-2026.log | grep CRITICAL
[INFO] Monitoring latest CVEs — 2026 Security Research Database [ALERT] 26 critical vulnerabilities tracked across major systems [WARN] Multiple Pre-Auth RCE vectors identified — patch immediately
18RCE
3SQLi
4Code Exec
26Total CVEs
# CVE ID Produk / Target Dampak Severity
1CVE-2026-1731BeyondTrust Remote Support / PRAPre-auth RCE, unauthenticatedCRITICAL
2CVE-2026-24156NVIDIA DALIArbitrary code executionHIGH
3CVE-2026-25731CalibreSSTI †' code executionCRITICAL
4CVE-2026-32157Microsoft Remote Desktop ClientRCEHIGH
5CVE-2026-35643OpenClawArbitrary code executionHIGH
6CVE-2026-40044PachnoPHP deserialization †' RCECRITICAL
7CVE-2026-55200libssh2Potential RCE / memory corruptionHIGH
8CVE-2026-57087Windows Media FoundationRCEHIGH
9CVE-2026-60137WordPress Core — WP2ShellSQLi; pre-auth RCE chainCRITICAL
10CVE-2026-63030WordPress Core — WP2ShellREST API route confusion †' pre-auth RCECRITICAL
11CVE-2026-64966ATutorPath traversal †' RCECRITICAL
12CVE-2026-65660Microsoft SharePoint ServerCode injection †' RCECRITICAL
13CVE-2026-6875ServiceNow AI PlatformSandbox escape †' code executionCRITICAL
14CVE-2026-70311Microsoft Office WordCode executionHIGH
15CVE-2026-70570Windows RRASRCECRITICAL
16CVE-2026-73325Fujitsu OneCompressionArbitrary code executionHIGH
17CVE-2026-75021fastify-cliNode Inspector †' RCECRITICAL
18CVE-2026-76841XinferenceArbitrary Python/code executionHIGH
19CVE-2026-80074Microsoft Remote Desktop ClientRCEHIGH
20CVE-2026-80077Microsoft Remote Desktop ClientRCEHIGH
21CVE-2026-85046Google ChromeSandbox/code executionCRITICAL
22CVE-2026-88772Citrix NetScaler ADC/GatewayRCE / DoSCRITICAL
23CVE-2026-9586Sangoma Switchvox SMBSQLi †' arbitrary code executionCRITICAL
24CVE-2026-100580OpenClawRCE via cron toolCRITICAL
25CVE-2026-100682Budibase ServerArbitrary file write †' RCECRITICAL
26CVE-2026-11729IBM MQ JavaUnsafe deserialization †' RCECRITICAL
[*] Data ini dipublikasikan untuk tujuan edukasi keamanan siber. Selalu lakukan patching dan mitigasi sesuai advisory resmi dari vendor. // Stay responsible.

Skills & Tutorials

Berbagi pengetahuan tentang Web Development, Penetration Testing, Bug Hunting, dan OSINT — dari dasar hingga expert level.

◇ Web Developer
☡ Pentester
☢ Bug Hunter
☠ OSINT Analyst
❮/❯

Web Development — Expert

01

REST API Security — JWT, OAuth2 & CSRF

EXPERT

Implementasi autentikasi aman menggunakan JWT dengan refresh token rotation, proteksi OAuth2 flow, dan mitigasi CSRF pada aplikasi modern (Node.js / Laravel).

// Secure JWT verification example
const token = jwt.verify(req.headers.authorization, process.env.SECRET, { algorithms: ['HS256'] });
Node.jsJWTOAuth2
02

SQL Injection Prevention — Parameterized Queries

INTERMEDIATE

Cara benar mencegah SQL Injection dengan prepared statements, ORM query binding, dan input sanitization. Termasuk bypass WAF yang perlu diantisipasi developer.

// Safe query — PHP PDO
$stmt = $pdo->prepare('SELECT * FROM users WHERE id = ?');
$stmt->execute([$id]);
PHPPDOSQL
03

Secure File Upload — Bypass Prevention

EXPERT

Validasi file upload yang benar: MIME type checking, magic bytes validation, rename file, isolasi storage, dan mencegah webshell upload bypass yang umum ditemukan saat pentest.

# Check magic bytes — Python
magic = open(file, 'rb').read(4)
if magic != b'\xff\xd8\xff\xe0': raise ValueError('Not JPEG')
PythonFile UploadSecurity
04

XSS Prevention & Content Security Policy

INTERMEDIATE

Mencegah Cross-Site Scripting melalui output encoding, DOM XSS mitigation, implementasi CSP header yang tepat, dan sanitasi HTML dengan DOMPurify.

// CSP Header — Express.js
res.setHeader('Content-Security-Policy',
  "default-src 'self'; script-src 'self' 'nonce-xxx'");
XSSCSPDOMPurify
☡

Penetration Testing

01

Web Recon — Subdomain Enumeration & OSINT

EXPERT

Teknik recon komprehensif menggunakan subfinder, amass, httpx, nuclei untuk menemukan attack surface. Integrasi dengan Shodan dan Censys untuk passive recon.

# Full recon pipeline
subfinder -d target.com | httpx -silent | nuclei -t exposures/
ReconSubfinderNuclei
02

SSRF Exploitation — Internal Network Access

EXPERT

Cara menemukan dan mengeksploitasi Server-Side Request Forgery untuk mengakses metadata cloud (AWS/GCP), internal services, dan pivot ke network internal.

# AWS metadata via SSRF
curl "http://target.com/proxy?url=http://169.254.169.254/latest/meta-data/"
SSRFAWSCloud Pentest
03

Burp Suite — Advanced Techniques

EXPERT

Penggunaan Burp Suite Pro secara advanced: custom extensions dengan Jython, active scanning, intruder payload generation, dan automation dengan Burp REST API.

Burp SuiteJythonActive Scan
04

Exposed Credentials & Sensitive Data Hunting

INTERMEDIATE

Teknik menemukan exposed credentials di Git repos, environment files, backup files, dan cloud storage. Tools: trufflehog, gitleaks, s3scanner, wayback machine.

# Hunt secrets in git history
trufflehog git https://github.com/target/repo --json
TruffleHogGitLeaksS3
☢

Bug Bounty Hunting

01

Menulis Laporan Bug yang Impactful

EXPERT

Cara menulis bug report yang diterima dan dihargai tinggi: proof-of-concept yang jelas, impact assessment, CVSS scoring, dan langkah reproduksi yang detail.

Report WritingCVSSPoC
02

IDOR — Business Logic Vulnerabilities

EXPERT

Menemukan Insecure Direct Object Reference dan Business Logic flaws yang sering terlewat scanner otomatis. Teknik manual testing pada parameter ID, UUID, dan API endpoints.

IDORBusiness LogicAPI
03

Government VDP — Responsible Disclosure

EXPERT

Panduan melaporkan kerentanan pada sistem pemerintah Indonesia: BSSN VVIP, Diskominfo, dan instansi lainnya. Etika, timeline, dan komunikasi yang tepat dengan tim security pemerintah.

BSSNGov VDPEthics
☠

OSINT — Open Source Intelligence

01

Digital Footprint Analysis

EXPERT

Mengumpulkan dan menganalisis jejak digital target menggunakan Maltego, theHarvester, SpiderFoot, dan teknik Google dorking untuk intelligence gathering secara pasif.

# Google dork — exposed configs
site:target.com ext:env | ext:config | ext:log
MaltegotheHarvesterDorking
02

Shodan & Censys — Internet Scanning

INTERMEDIATE

Memanfaatkan Shodan, Censys, dan FOFA untuk menemukan exposed services, default credentials, dan misconfigured systems milik target secara non-invasif.

# Shodan CLI search
shodan search "org:target.com port:8080" --fields ip_str,port
ShodanCensysFOFA
03

Social Media & Username Recon

INTERMEDIATE

Teknik username enumeration across platforms, reverse image search, email hunting (hunter.io), dan social engineering intelligence menggunakan tools open source.

# Username recon — Sherlock
python3 sherlock.py fahmi_x12 --timeout 5
SherlockHunter.ioSOCMINT

Contact

root@fahmi_haxor:~# ./connect.sh --target psychoxploit
$ initializing secure channel...
$ connection established ✓
$ ready to collaborate. –

> Send Message